| Configuring Secure Shell (SSH) |
| Terminology |
|
|
N o t e | SSH in the HP Procurve Series 4100GL switches is based on the OpenSSH |
| software toolkit. For more information on OpenSSH, visit http:// |
| www.openssh.com. |
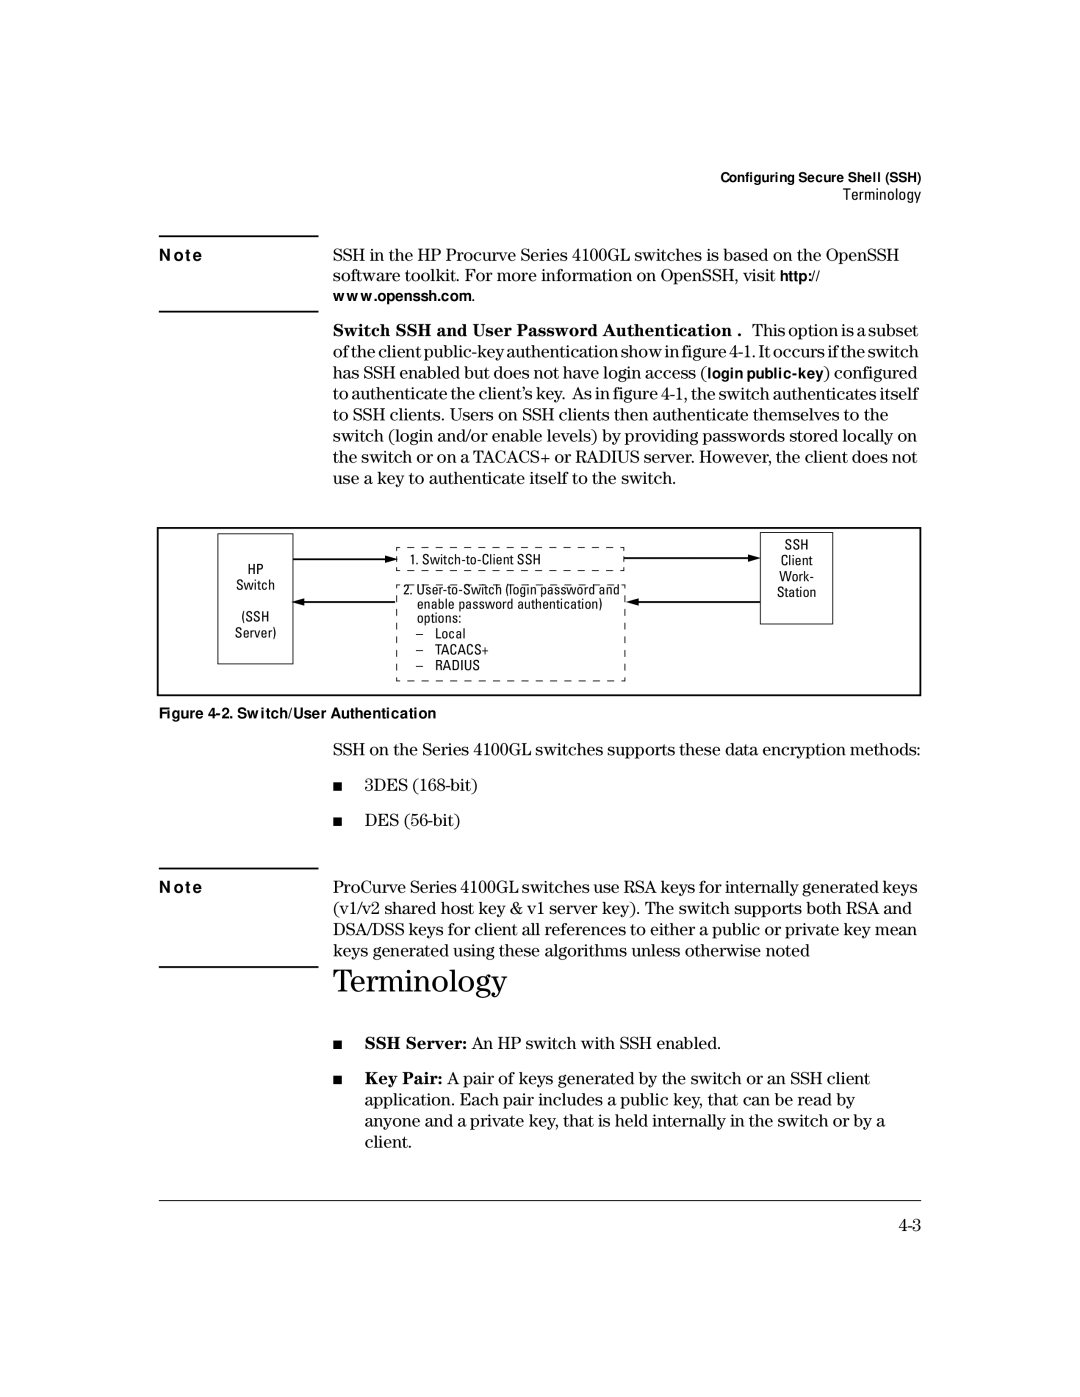
| Switch SSH and User Password Authentication . This option is a subset |
| |
| of the client |
| has SSH enabled but does not have login access (login |
| to authenticate the client’s key. As in figure |
| to SSH clients. Users on SSH clients then authenticate themselves to the |
| switch (login and/or enable levels) by providing passwords stored locally on |
| the switch or on a TACACS+ or RADIUS server. However, the client does not |
| use a key to authenticate itself to the switch. |
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
HP |
|
|
|
|
| 1. | |||||||||||||||||||||||||||||||||||||||||||
|
|
|
| ||||||||||||||||||||||||||||||||||||||||||||||
|
|
|
| ||||||||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
| |
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
| |
Switch |
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
| |||||||||||||||
|
|
| 2. | ||||||||||||||||||||||||||||||||||||||||||||||
(SSH |
|
|
|
|
|
| enable password authentication) | ||||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
| ||||||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
| options: | |||||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
| ||||||||||||||||||||||||||||||||||||||||||||
Server) |
|
|
|
|
|
| – | Local | |||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
| ||||||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
| ||||||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
|
| – | TACACS+ | |||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
|
| |||||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
|
| – | RADIUS | |||||||||||||||||||||||||||||||||||||||||
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
SSH
Client
Work-
Station
Figure 4-2. Switch/User Authentication
| SSH on the Series 4100GL switches supports these data encryption methods: | |
| ■ | 3DES |
| ■ | DES |
|
| |
N o t e | ProCurve Series 4100GL switches use RSA keys for internally generated keys | |
(v1/v2 shared host key & v1 server key). The switch supports both RSA and DSA/DSS keys for client all references to either a public or private key mean keys generated using these algorithms unless otherwise noted
Terminology
■ SSH Server: An HP switch with SSH enabled.
■ Key Pair: A pair of keys generated by the switch or an SSH client application. Each pair includes a public key, that can be read by anyone and a private key, that is held internally in the switch or by a client.